Built by a cybersecurity company.
Timberline is developed and operated by Sidechain Security, a team that designs and operates security programs for enterprise clients.
Meet Sidechain Security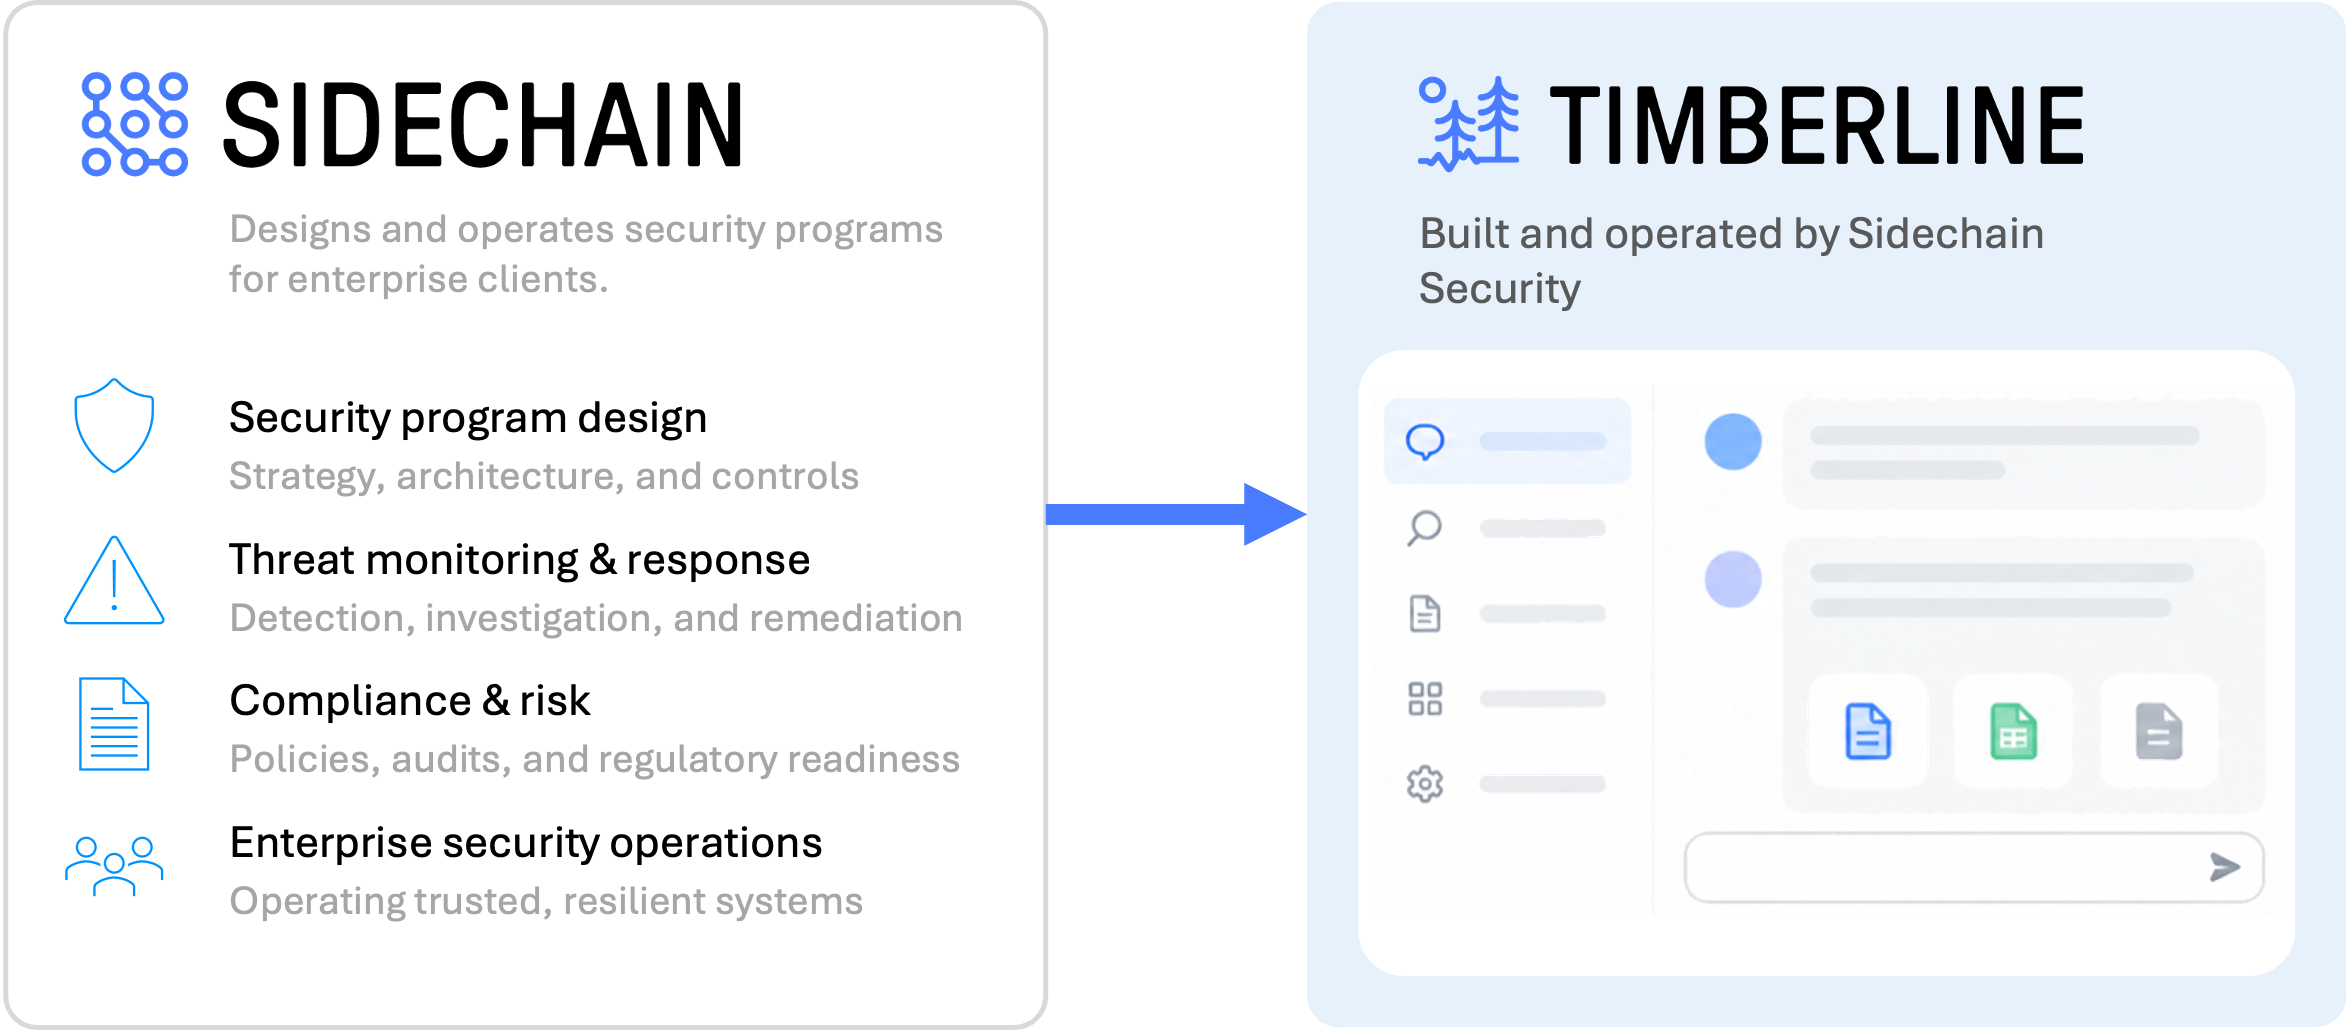
 Request a demo
Built for sensitive healthcare work from the beginning, with dedicated environments, encryption, access controls, and data usage you control.
Talk with Timberline
Timberline is developed and operated by Sidechain Security, a team that designs and operates security programs for enterprise clients.
Meet Sidechain SecurityCustomer workloads are segmented and single-tenant, with no shared data, hard network separation, and dedicated encryption keys.
Explore the architecture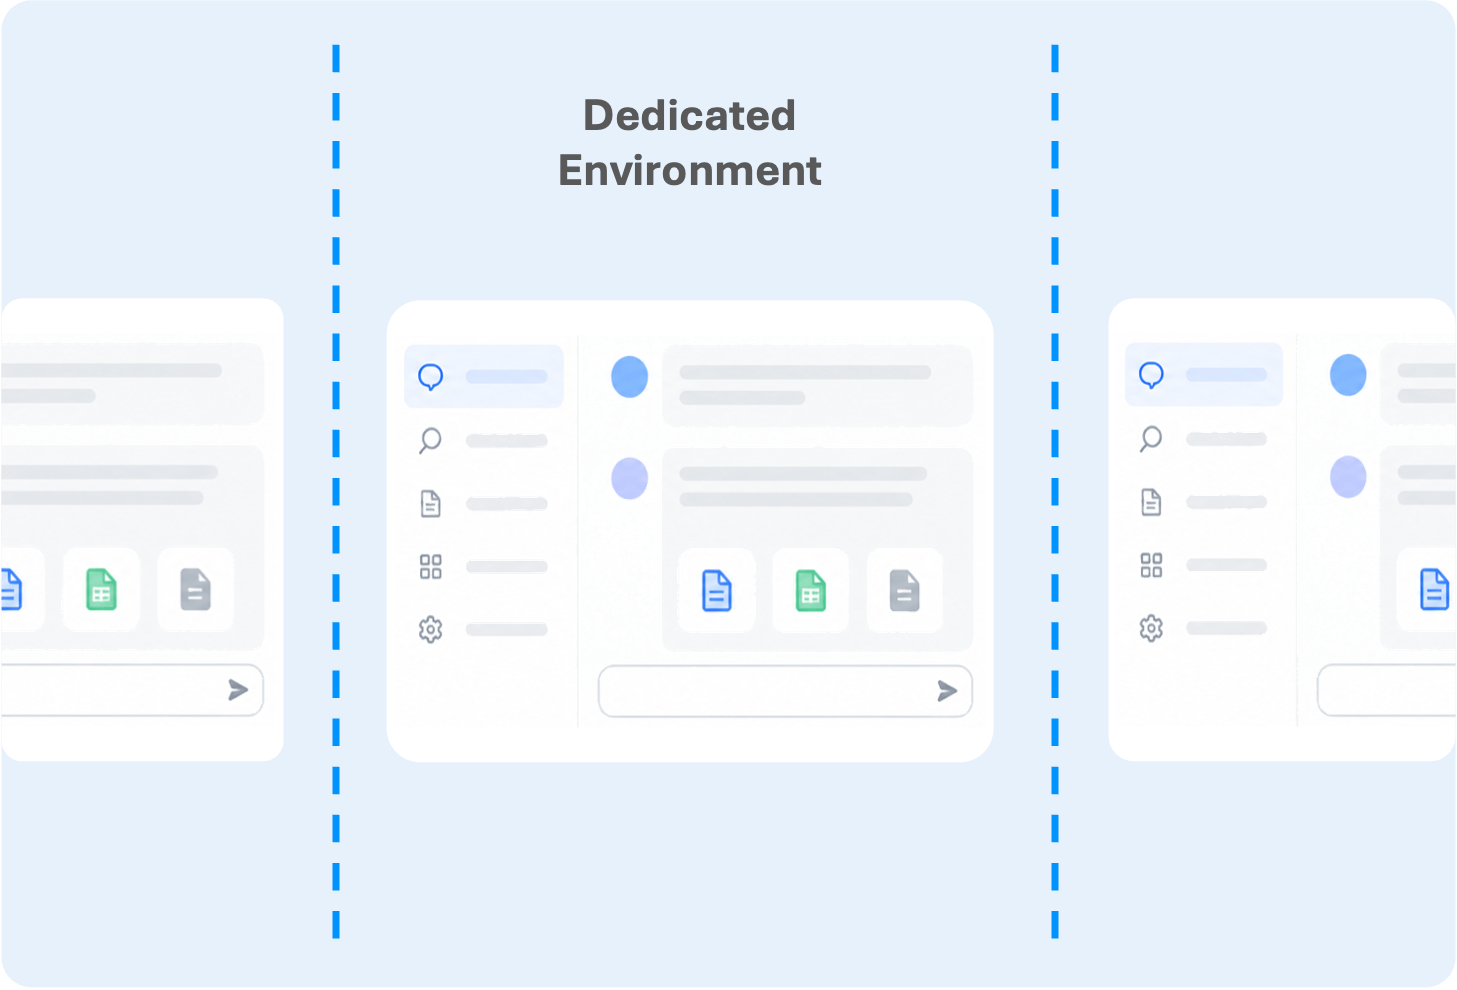
Customer information, including prompts, chats, documents, and saved data, are never used for training or sent to third-party AI services.
Explore data and privacy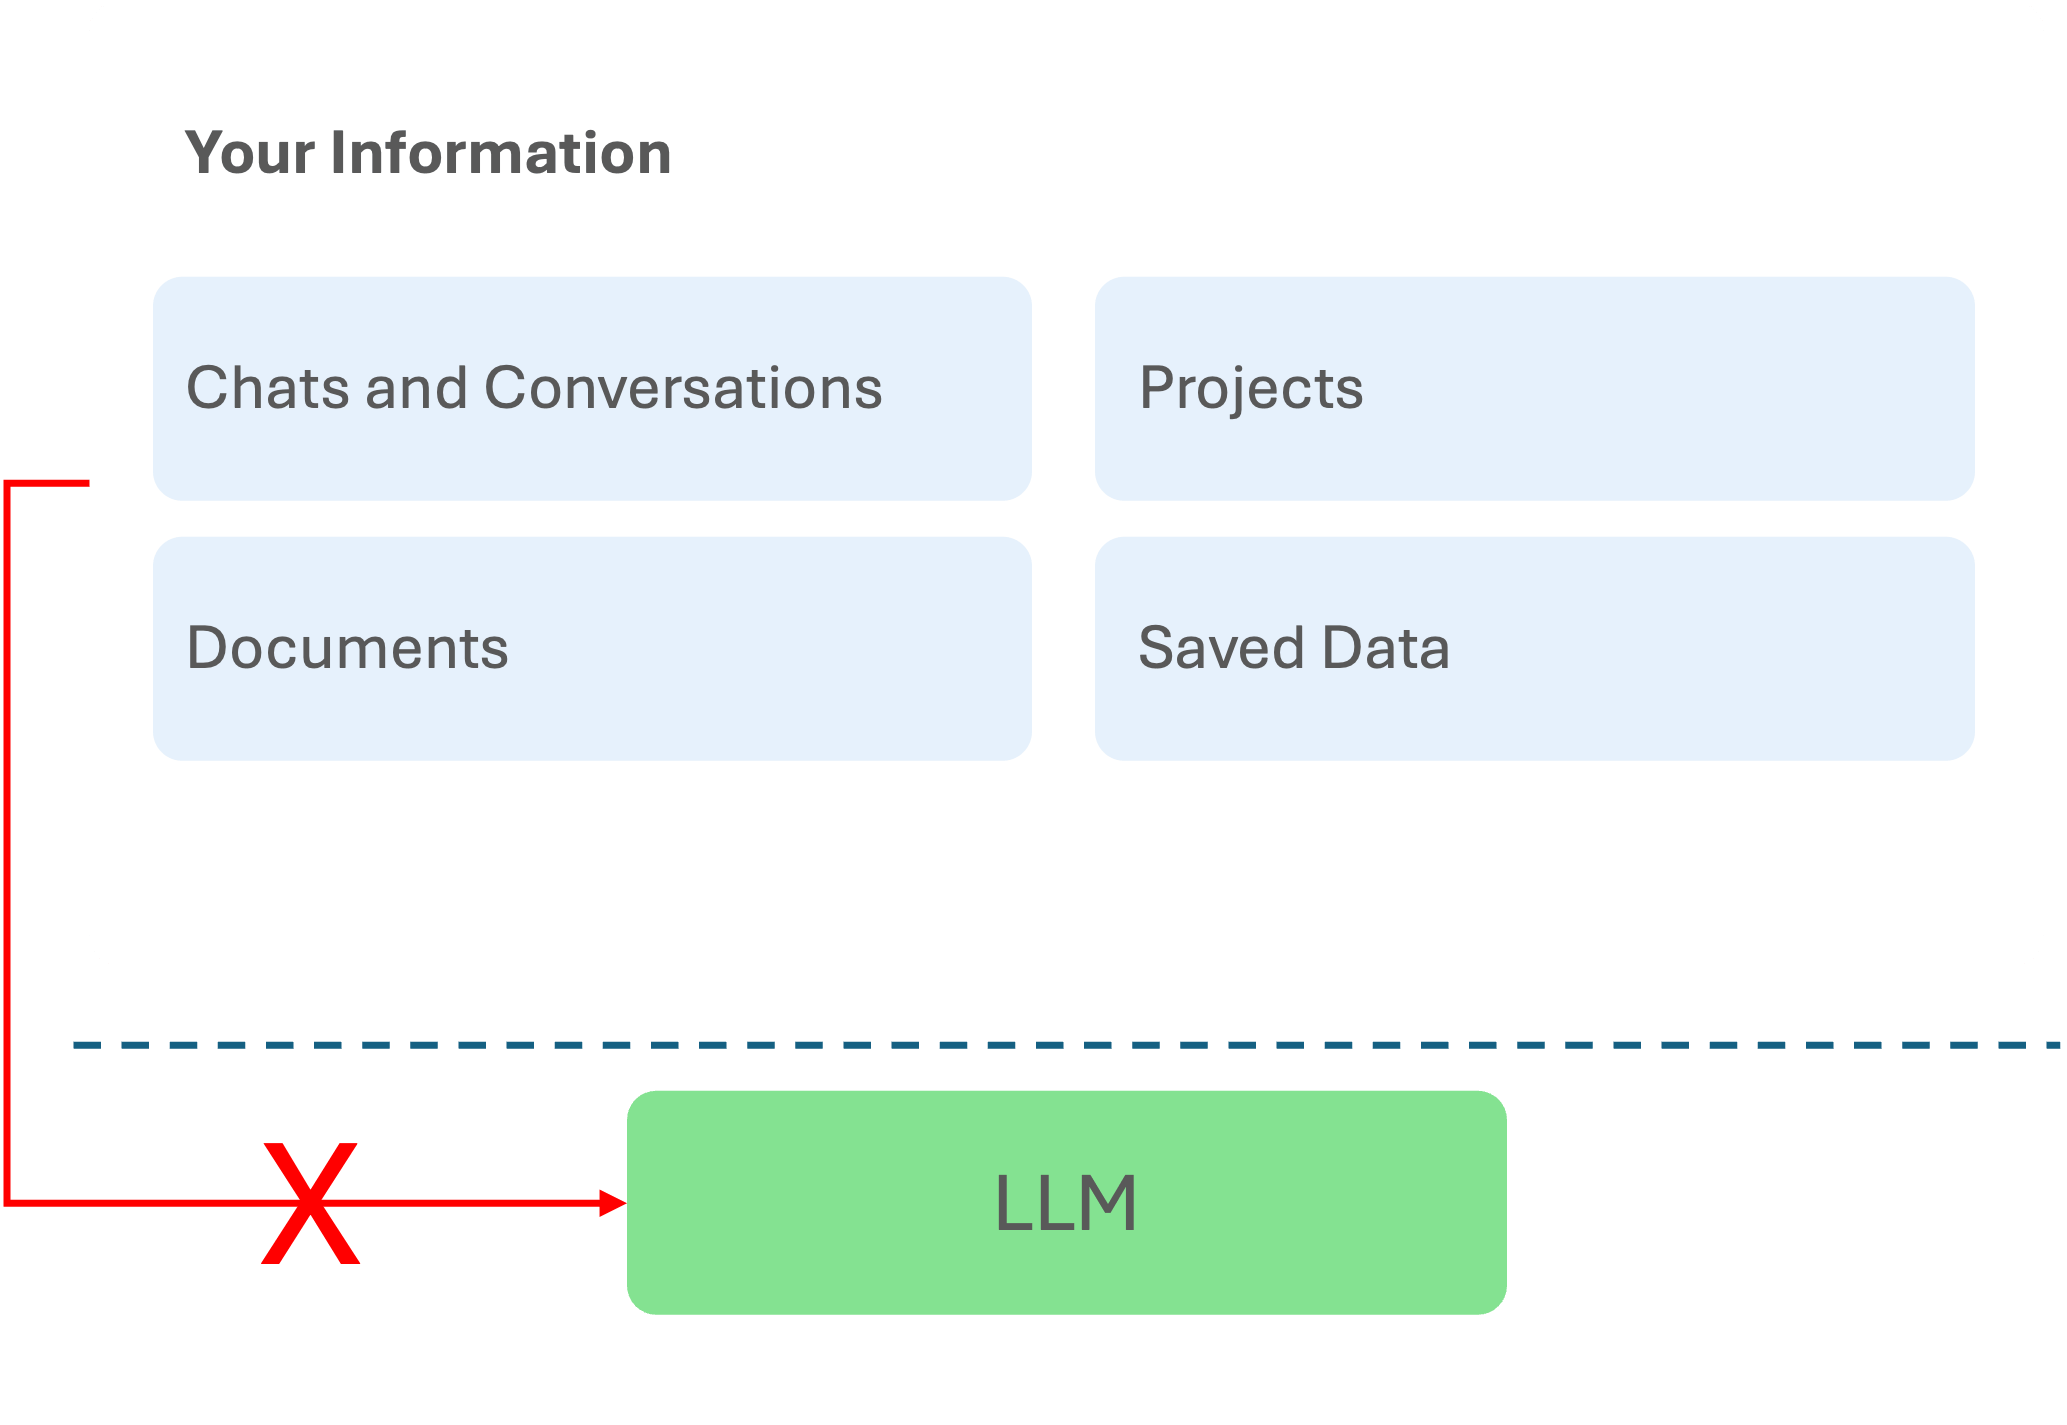
Timberline is built for healthcare organizations that need to work with protected health information. We enter into a Business Associate Agreement that defines how PHI may be used, protected, and handled.
Explore BAA and PHIWe did not start with an AI product and ask how to secure it.
We started with the security requirements, and built the AI platform to spec.
Each Timberline customer operates within a separate tenant environment with its own access controls, application context, customer data, and AI workloads. Customer information is not exposed to other Timberline customers, and access between tenant environments is not permitted.
The goal is simple: your organization’s work stays inside your organization’s boundary. The one deliberate exception is web search: when an administrator enables it, search queries go to a public search provider with identifying details removed first.
Timberline is designed around dedicated customer environments rather than a single shared workspace for every customer.
Each tenant has its own application and data boundary, with customer-specific identity, permissions, configuration, and AI context. These are logically isolated environments; underlying physical infrastructure may be shared.
Yes. Timberline is designed for healthcare organizations that need to use AI with protected health information.
When Timberline acts as a business associate, we can enter into a Business Associate Agreement governing the permitted use and protection of PHI. We also work with customers to confirm appropriate access, retention, integration, and security controls before PHI is introduced.
Customer information is processed within Timberline’s controlled cloud environment and the services required to provide the platform.
We document the hosting architecture, processing locations, and relevant subprocessors as part of security review so customers can understand where their information is handled.
Retention is governed by the terms established for the customer environment and contractual requirements.
Timberline is designed to support defined retention periods and deletion of customer information when it is no longer required. Specific retention and deletion requirements can be addressed as part of deployment and security review.
No. Customer data is not used to train shared models for Timberline or for other customers.
Information provided to Timberline is used to deliver the service to your organization, subject to the controls and terms governing your environment.
Access is limited to authorized users and governed by identity, permissions, and administrative controls.
Within the customer environment, users only have access to the work and resources they are permitted to use.
Connections are explicit and controlled. Customers determine which systems Timberline can access and what information those connections make available.
An integration does not automatically give Timberline unrestricted access to the underlying system. Access should be scoped to the information and permissions required for the intended use.